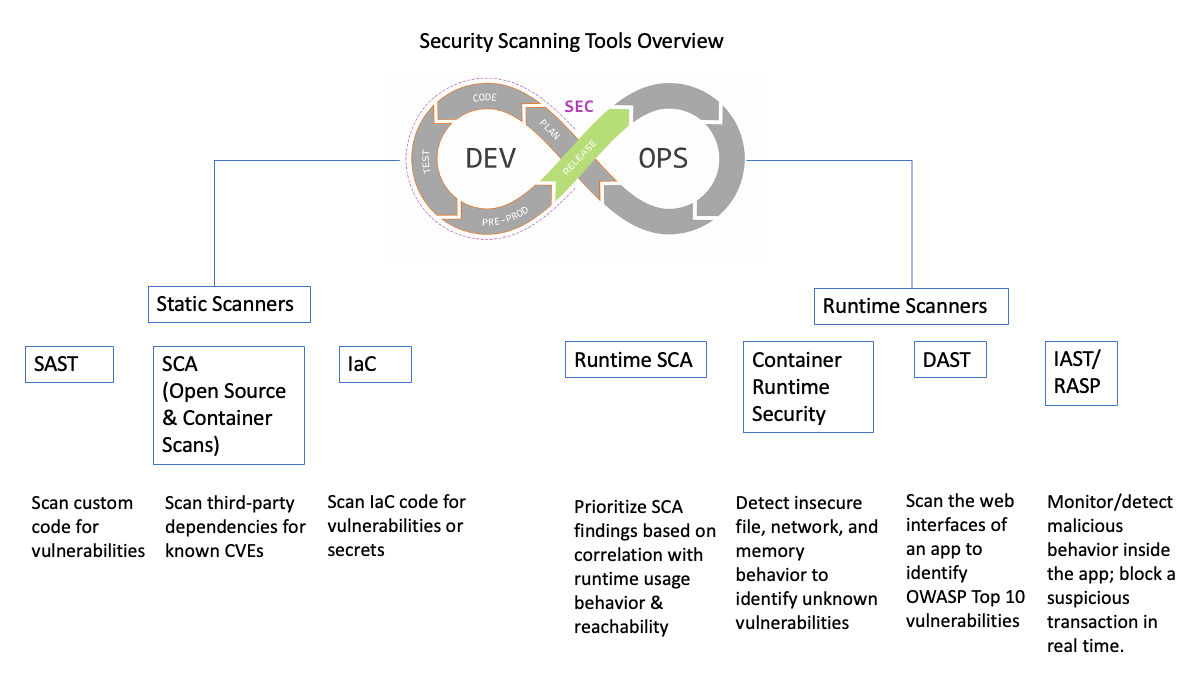
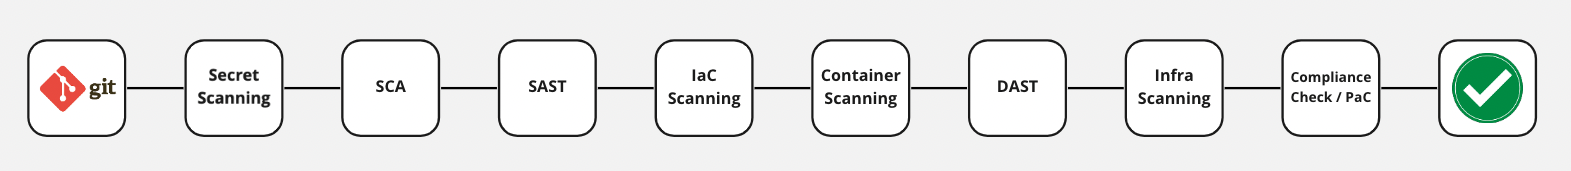
General
Repositories
- awesome-devsecops: Curating the best DevSecOps resources and tooling 🌟 (Recommended)
- awesome-iam: 👤 Identity and Access Management knowledge for cloud platforms 🌟 (Recommended)
- Blog - The DevSec Blueprint: a comprehensive, free, and open-source learning guide designed to equip you with the essential skills and knowledge needed to transition into or grow your Cloud Security Development & DevSecOps career.
- dynamic-analysis: A curated list of dynamic analysis tools and linters
- GitHub - DevSecOps-MaturityModel: Provides opportunities to harden DevOps strategies and shows how these can be prioritized. Go to https://dsomm.owasp.org.
- GitHub (OWASP) - DevSecOps Guideline: The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
- OWASP - Free for Open Source Application Security Tools: the following lists of automated vulnerability detection tools that are free for open source projects have been gathered together here to raise awareness of their availability. 🌟 (Recommended)
- OWASP - Projects: The OWASP Foundation gives aspiring open source projects a platform to improve the security of software
- OWASP - Source Code Analysis Tools: The collections of SAST which organized by OWASP and community contribution
- static-analysis: A curated list of static analysis (SAST) tools and linters 🌟 (Recommended)
- Hahwul/DevSecOps: Collection and Roadmap for everyone who wants DevSecOps. 🌟 (Recommended)
- awesome-threat-modelling: A curated list of threat modeling resources for learning Threat modeling and initial phases of security review.
Landscape
- SonarType - DevSecOps Reference Architecture 🌟 (Recommended)
- OpenSSF - Projects 🌟 (Recommended)
- OWASP - Projects 🌟 (Recommended)
Technique
- Outpost24 - What is best for application security testing: SAST, DAST, or SCA
- Microsoft - Zero Trust DevSecOps
- DoD - DoD Enterprise DevSecOps Source Diagrams - Diagram to visual the DevSevOps Enterprise Architecture of DoD CIO 🌟 (Recommended)
- OWASP - OWASP DevSecOps Verification Standard 🌟 (Recommended)
- Dev.to - WireGuard DoV (DNS-over-VPN)
Technology
- Medium - Building end-to-end DevSecOps for AWS Migration: Security at Entry Level with open source SCA, SAST and DAST tools
- Medium - Establishing an Enterprise-Ready DevSecOps CI/CD Pipeline on GitHub Actions on Google Cloud
- AWS - Building an end-to-end Kubernetes-based DevSecOps software factory on AWS 🌟 (Recommended)
- Wiz.io - Top Open-Source DevSecOps Tools and Security Practices 🌟 (Recommended)
- Wiz.io - Guide to SBOM Tools: 5 Picks for Enterprise Security Teams 🌟 (Recommended)
Stories
Papers and Researching
- Arxiv - AI for DevSecOps: A Landscape and Future Opportunities
- MDPI - Evolution of DevSecOps and Its Influence on Application Security: A Systematic Literature Review
- SLSA (Supply-chain Levels for Software Artifacts)
Community
- OWASP: The world’s largest nonprofit foundation dedicated to improving software security through open-source collaboration, education, and innovation.
- OpenSSF: The Open Source Security Foundation. Powered by The Linux Foundation
DevSecOps Tools
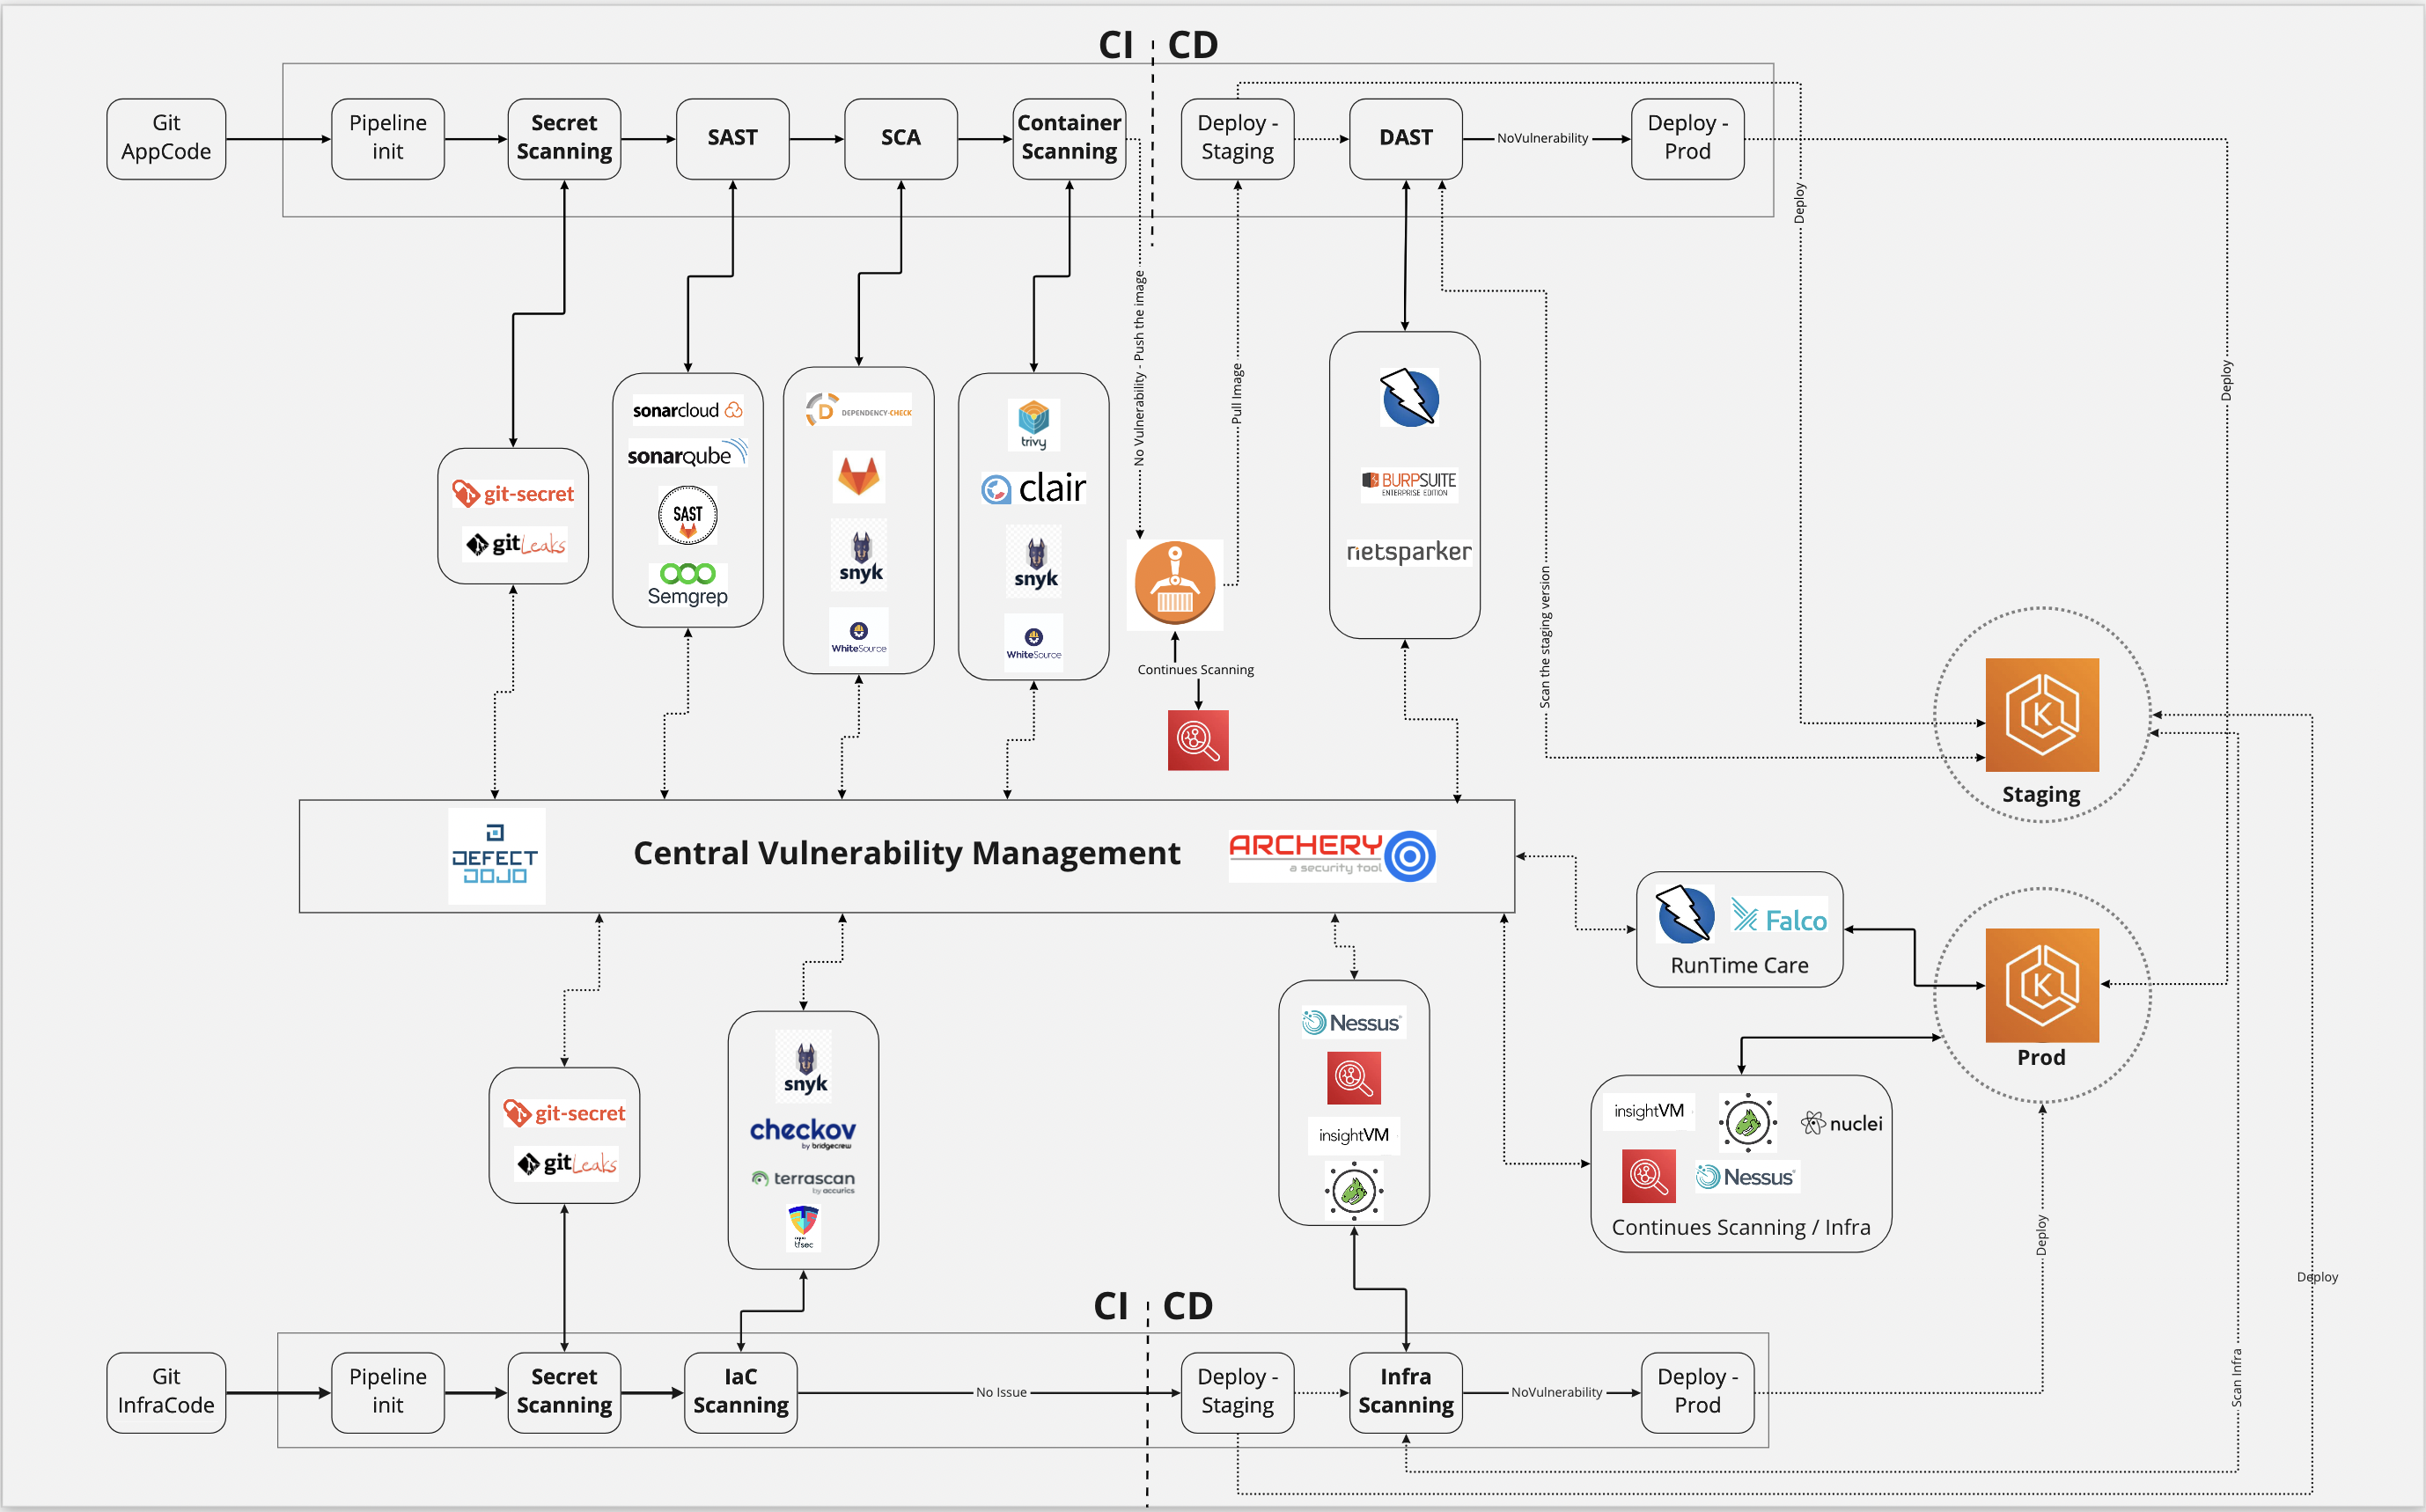
Source: OWASP DevSecOps Guideline
AI & Machine Learning
- openappsec: a machine learning security engine that preemptively and automatically prevents threats against Web Application & APIs.
SAST
- Sonarqube: An on-premise analysis tool designed to detect coding issues 🌟 (Recommended)
- Sonar Rule: The collections of rule integrate into Sonarqube Server
- trivy: Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more 🌟 (Recommended)
- GitGuardian ggshield: a CLI application that runs in your local environment or in a CI environment to help you detect more than 500+ types of secrets. 🌟 (Recommended)
- bearer: Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
DAST
- Nettacker : Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
- nuclei : Fast and customizable vulnerability scanner based on simple YAML based DSL. Doc and Cloud Platform 🌟 (Recommended)
- zaproxy : The ZAP core project 🌟 (Recommended)
Dependencies Check
- DependencyCheck: a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
- dependency-track: an intelligent Component Analysis platform that allows organizations to identify and reduce risk in the software supply chain.
Software Supply Chain
- cosign: Code signing and transparency for containers and binaries
- Syft is a widely used open-source CLI tool from Anchore that generates SBOMs from container images and filesystems.
- sbom-tools: Semantic SBOM/CBOM diff, quality scoring, and analysis tool. Compare, validate, and grade software and cryptographic bills of materials across CycloneDX and SPDX formats.
Vulnerability Hub & Security Platform
- django-DefectDojo: Open-Source Unified Vulnerability Management, DevSecOps & ASPM
- wazuh: The Open Source Security Platform. Unified XDR and SIEM protection for endpoints and cloud workloads.
- archerysec: ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
- faraday: Open Source Vulnerability Management Platform
- openclarity: an open source platform built to enhance security and observability of cloud native applications and infrastructure